ZX PLATFORM · HYPER SANDBOX

Unknown threats,
one unified platform
for precise detection.

Keep the security stack you already have. Just add an engine for new and unknown threats.
It plugs into email, network, cross-domain transfer and endpoints.

Free, no sign-up · Threat analysis and disarm (CDR) · Originals deleted automatically after processing

0.27sAverage analysis time per fileKBeT V&V test certified · competitors avg. 60 s
99%Detection rate for recent malware250,000 recent MalwareBazaar samples (2022 onward)
1.0MFiles processed per dayOn a single 8-core server · competitors avg. 40,000
ZX PLATFORM

Four layers,
watched on one screen

Files coming in through email, network, cross-domain transfer and endpoints are all inspected by a single analysis engine.
Unknown threats are isolated the moment they're found.

  • Threat detected
  • Isolated
Threat names shown are examples.
Email
Network
Cross-domain
Endpoint
ZX PLATFORM · CAPABILITIES

Built on a single Hyper Sandbox:
ZX PLATFORM capabilities

LAYER 03Deployment · operations
  • WEB CONSOLE · dashboard · reports · policies
  • On-premises · cloud · redundancy
  • ZX CORE SDK · API · OEM
  • Cloud PoC
  • U100 – U5000+
LAYER 02Analysis · disarm · blocking
  • Pre-filter · reputation · URL · YARA
  • AI risk scoring
  • MITRE ATT&CK mapping
  • ZX CDR precision disarm
  • Pre-execution detection
LAYER 01Unified analysis across security layers
  • Email
  • Network
  • Cross-domain
  • Endpoint
  • Ransomware blocking · recovery
  • IOC · verdict evidence report
  • 30-day evaluation API
  • Audit log · quarantine
Keep your existing security gearMail securityNGFW · UTMCross-domain solutions
SECURITY OPERATIONS INTEGRATION
Plugs straight into your SOCSOARSIEMEPP · EDR
ZX PLATFORM
MAIL TRANSFER AGENT

MTA integration

Integrates in front of the mail server as an MTA. Attachments, archives and URLs in message bodies are judged by the Hyper Sandbox before they reach the inbox. Remaining threats are removed with CDR, and malicious mail is blocked and quarantined.

  • Hyper Sandbox first, then CDR disarm: verified twice before delivery
  • Anti-spam API integration also supported
  • Keep your existing mail security and add only an analysis layer
  • Processed in under a second, so no mail delivery delay
Starts as soon as you drop
Sample result
Risk 10invoice_1007.xls0.52 s
Clean 0meeting_notes_Q2.hwp0.21 s
Disarmedquote_1016_safe.docxGet ↓
See a sample analysis result →
400K+New unidentified malicious files created every day (based on AV-TEST data)91%Successful cyberattacks that start with email (US CISA)
COMPETITIVE ANALYSIS

Depth of analysis and speed, together

Competitive positioning map · analysis depth × processing speed

Joe SandboxJoe SecurityJoe SandboxDeep-analysis sandbox that runs samples across multiple OSesAnalysis depth High · Speed LowVM-RayVMRayVMRay AnalyzerHypervisor-based dynamic analysis sandboxAnalysis depth High · Speed LowTrellix MVXTrellix (formerly FireEye)Multi-Vector Execution engineVirtual execution analysis engine built into network and mail appliancesAnalysis depth High · Speed LowAdvanced WildFirePalo Alto NetworksAdvanced WildFireCloud malware analysis service integrated with the firewallAnalysis depth High · Speed MediumANY.RUNANY.RUNANY.RUN Interactive SandboxInteractive online sandbox operated hands-on by analystsAnalysis depth Medium · Speed LowCheck Point TECheck Point SoftwareThreat EmulationThreat emulation (sandbox) at the gateway and in the cloudAnalysis depth Medium · Speed MediumRF TriageRecorded FutureRecorded Future TriageCloud sandbox for fast triage of large sample volumesAnalysis depth Medium · Speed HighOPSWAT AetherOPSWATMetaDefender AetherEmulation-based adaptive sandboxAnalysis depth Low · Speed HighFortiSandbox 5.0FortinetFortiSandbox 5.0Sandbox integrated with Fortinet security appliancesAnalysis depth Low · Speed MediumZscaler SandboxZscalerZscaler Cloud SandboxInline sandbox within a cloud security serviceAnalysis depth Low · Speed HighZX CORE™HYPER SANDBOXAKDANZX CORE™ HYPER SANDBOXOur own lightweight hypervisor quickly observes OS and app behavior. 0.27 s per file on average (KBeT test).Analysis depth High · Speed High

* ZX CORE is based on our technical specifications. Other vendors are based on their public materials; implementation details may vary by version and license.

ZX PLATFORM

From inbound file to PC execution,
one engine guards four stages

Known threats are filtered first, and only new threats go to the Hyper Sandbox for a verdict.
Documents people need to open are disarmed and delivered.

EmailMTA, anti-spam APINetworkICAP, REST APICross-domainREST APIEndpointEDR, XDR
CORE TECHNOLOGY

Three technologies that draw out even hidden malicious behavior

01AGENTLESS

Lightweight hypervisor analysis

Fast analysis · agentless

Observes behavior at the hypervisor layer, with no agent inside the VM.

  • Windows · Office · HWP
  • ZX lightweight hypervisor
  • Hardware
02FORCED EXECUTION

Forced execution of threat elements

Detects click-bait and social engineering

Force-runs buttons, hyperlinks, ClickFix and macros that wait for a click, drawing out hidden behavior.

  • 1 · Open the document
  • 2 · Force-run links and ClickFix
  • 3 · Expose hidden malicious behavior
03ADAPTIVE ENV

Adaptive analysis environment

Defeats VM detection and evasion

Changes the environment on every run and plants decoys, neutralizing techniques that spot a VM and hide.

  • Env A → Env B → Env C
  • Decoy documents placed
  • VM detection and evasion neutralized
12
Patents granted · 14 filed · 1 PCTVirtualized malicious-macro analysis · obfuscated script detection · CPU bursting detection · predictive memory detection · malicious URL detection
MITRE ATT&CK PROOF

ATT&CK Enterprise
Detection across all 14 tactics

505ATT&CK-mapped detectionsDetections with a technique ID, out of 576 detection algorithms
120ATT&CK techniquesIncluding sub-techniques · 69 parent techniques
14/14Tactics coveredEvery ATT&CK Enterprise tactic

Mapped detections per tactic · darker cells mean denser coverage

  • Reconnaissance3
  • Resource Development6
  • Initial Access37
  • Execution239
  • Persistence45
  • Privilege Escalation43
  • Defense Evasion299
  • Credential Access7
  • Discovery24
  • Lateral Movement11
  • Collection5
  • Command and Control65
  • Exfiltration6
  • Impact18

One detection can map to several techniques and tactics, so the per-tactic totals exceed the overall number of detections. Calculated by mapping analysis-engine detections to ATT&CK techniques.

Source: ZX-CORE mitre-attack-id, as of 2026.10.13 · Tactic assignment: attack.mitre.org technique pages · ATT&CK Enterprise 14-tactic framework

PRODUCTS

One platform, wherever you need it

Unified analysis server · enterprises · institutionsZX HUB

Analyzes files from every security layer centrally, in 0.27 s

  • Analysis filter + Hyper Sandbox + AI risk scoring
  • ZX CDR: removes only threat elements and delivers the document (option)
  • MTA · ICAP · REST API integration, redundant setup
  • Web console: dashboard · reports · policies
U100–U5000+On-premises · cloud
Learn more →
PC agent · personal · enterpriseZX ONE Agent

Judges files right before they open, and stops and rolls back ransomware

  • Hold execution → fast analysis → open or block
  • Real-time ransomware detection · instant blocking
  • Automatic recovery from protected local backup
  • Quarantine · scan exclusions · audit log
Personal: buy by cardZX HUB option
Learn more →
Developers · OEM partnersZX CORE SDK

Build the Hyper Sandbox into your own products and services

  • Evaluation API: 30-day free in-house testing
  • Mapped to 120 MITRE ATT&CK techniques
  • SDK: installed and run in the customer's environment
  • 4-core server, $0 license for analysis
30-day evaluation APIOEM agreement
Learn more →
ZX HUB web console · dashboard · reports · policies

WEB CONSOLE

From analysis to response, in one screen

See threat status and risk distribution, verdict evidence and MITRE ATT&CK, disarm history, and per-file-type policies in one console.
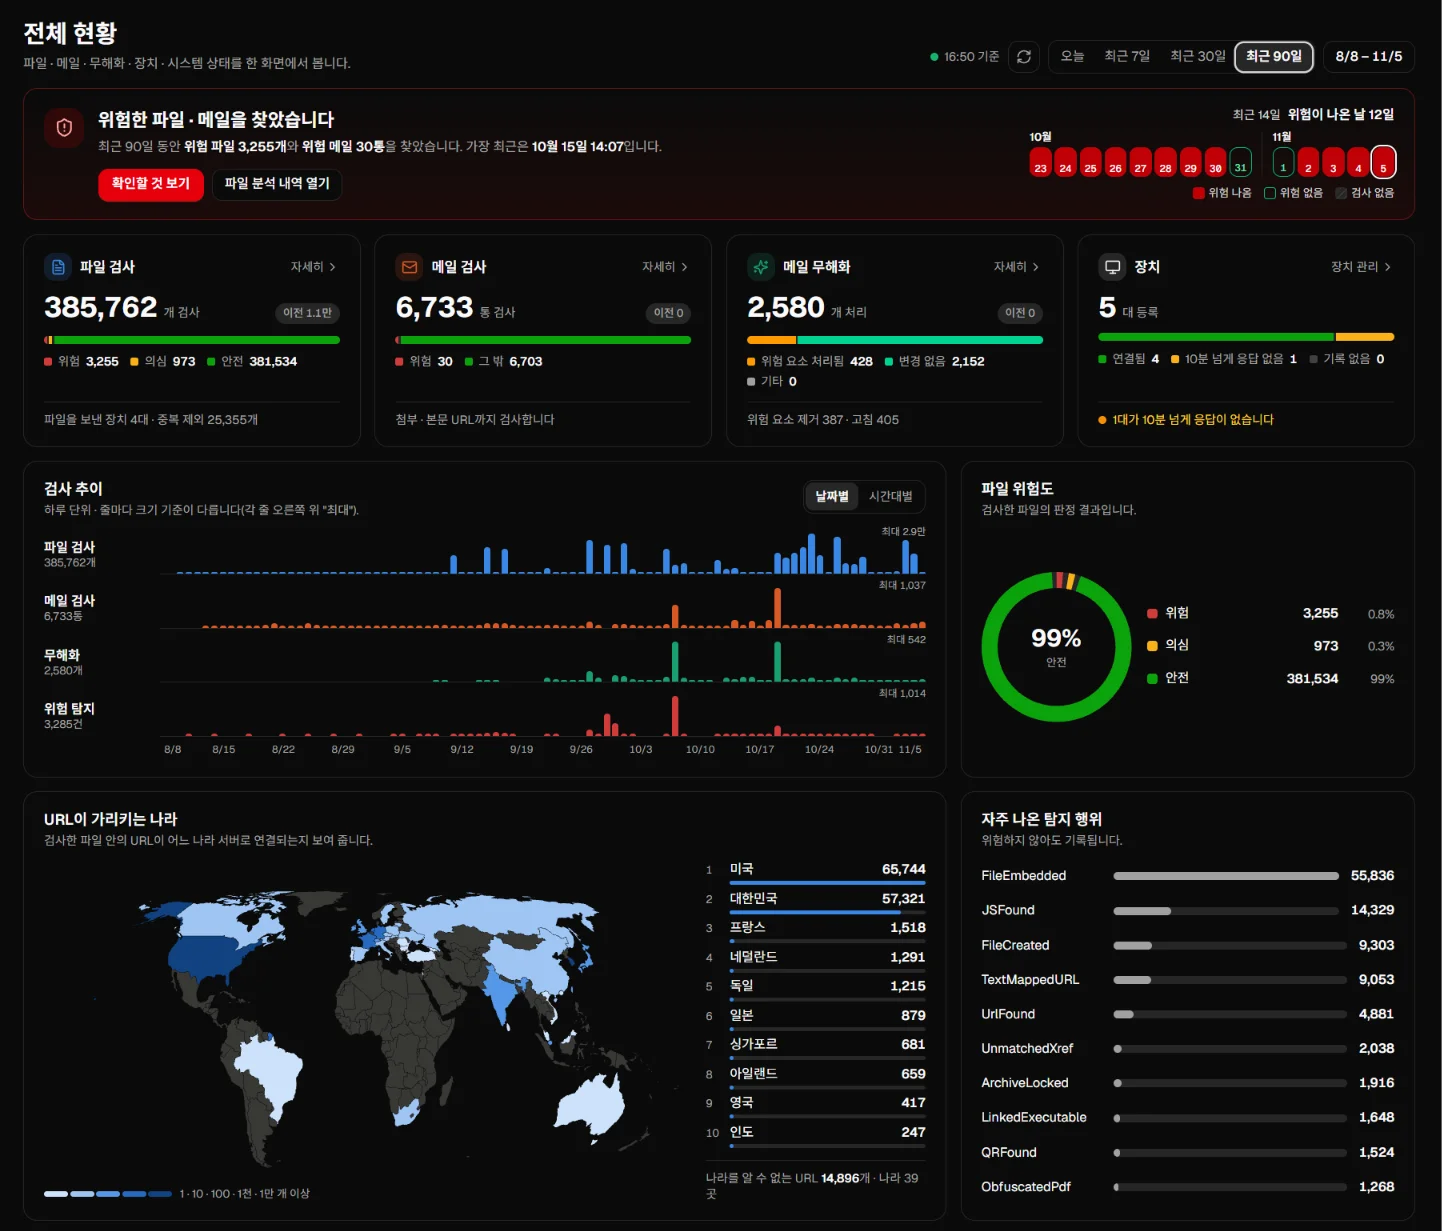
ZX HUB overview dashboard (dark theme). Shows risky file and mail alerts; file scan, mail scan, mail disarm and device status; scan trends; file risk levels; a map of the countries URLs point to; and the most frequent detected behaviors.
GET STARTED

Same engine. Start at the scale you need.

From testing a single file to rolling out across your organization, every verdict comes from the same Hyper Sandbox.

Anyone · no sign-up

Free trial

FreeRight on the web
  • Threat analysis and disarm (CDR)
  • Guests: 3 a day
  • Members: 20 a day · 200 a month, 90-day history
Personal PC

ZX ONE Personal

₩10,00050%₩5,000mo
  • 3 PCs
  • One-time payment · no auto-renewal
  • Verdict on the PC right before a file runs
Enterprise · public sectorSMBs to large enterprises · public institutions

ZX PLATFORM rollout

Contact usFrom the ₩10 million range
  • Configurations by scale, from ZX PLATFORM U100 to U5000+
  • Connects to existing equipment via MTA, ICAP or REST API
  • PoC right away in the cloud

Check it. Judge it.
Before you open it.

Try it now with a single suspicious file. It's free, no sign-up required.

ISOLATED · ZX COREHYPER SANDBOXJudged by behavior · 0.27 sMore +