ZX HUBUnified analysis server · enterprise · public sector
One high-speed
analysis server, shared
by every security layer.
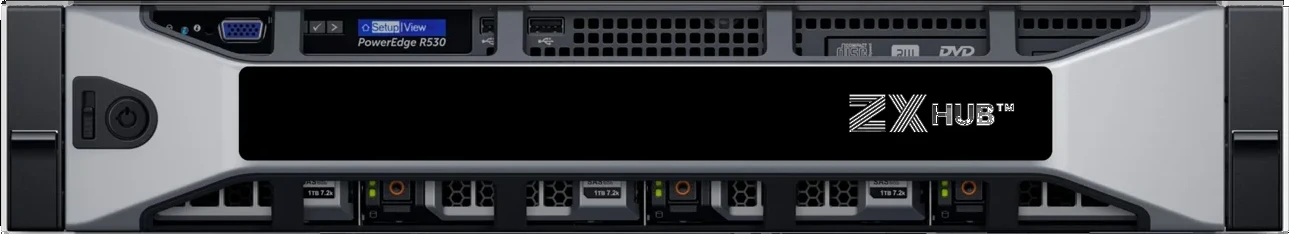
ZX HUB is a Hyper Sandbox server that centrally analyzes files from multiple layers.
It finds unknown threats and blocks, quarantines and disarms them together with your existing security systems.
Threats no longer arrive by just one route.
AI-enhanced UNKNOWN malware targets email, network, cross-domain transfer and endpoints all at once.
It slips past spam filters and firewalls and spreads across both internal and internet-facing networks. The later it's detected, the bigger the damage.
Email in particular is the most dangerous route, accounting for 91% of successful cyberattacks.(Source: U.S. CISA)
- EMAILSECURITY SOLUTIONSPassed spam filter
- NETWORKSECURITY SOLUTIONSPassed firewall · reputation
- CDS (cross-domain)SOLUTIONSPassed import check
- ENDPOINTSECURITY SOLUTIONSDetected only after it runs
Four layers,
watched on one screen
Files coming in through email, network, cross-domain transfer and endpoints are all inspected by a single analysis engine.
Unknown threats are isolated the moment they're found.
- Threat detected
- Isolated
What's in ZX HUB
Hyper Sandbox, ZX CDR and the web console in a single server.
Click HYPER SANDBOX to analyze a file right away.
- HYPER SANDBOXISOLATED · ZX CORERuns unknown threats and judges them by behavior · 0.27 s on average
- ZX CDRBehavior-basedPrecision disarm solution
- URL ANALYSISURL behavior analysisL0–L3 multi-layer scanning · forced hyperlink execution
- WEB CONSOLEStatistics dashboard · security policies · API management
Known threats fast, unknown threats deep
A pre-filter screens out known threats first; only the remaining files go to the Hyper Sandbox for deep analysis.
AI scores the risk and hands it to SOAR · SIEM as report.json.
File types HWP · DOC · XLS · PPT · PDF · ONE · VBS · JS · HTML · HTA · LNK · archives More on the technology →
Remove only the threat, deliver the document intact
Only macros, scripts, URLs and hyperlinks in the mail body and attachments are removed. Mail is delivered as usual. Documents aren't blocked outright, so users don't complain.
- MTA integration on the email layer
- Analyze, block and disarm in one pass
- Disarm report showing what was removed
- Original email · attachmentsEmail (MTA) · network-separation integrationMacrosScriptsURLsHyperlinks
Threat elements hidden in the body and attachments
- ZX CDRThreat removalBehavior analysis and disarm in one pass
Behavior-based precision content disarm
- Disarmed documentDelivered to the recipient as normalNeeded documents arrive intactMacrosScriptsURLsHyperlinks
Work continues with the cleaned file
From analysis to response in one flow
Handle file analysis reports and security policies in one flow in the web console.
Review verdict evidence, MITRE ATT&CK and IOCs, and set policies per file type.
Keep your existing investment, add only an analysis layer
Plug in through standard integrations; no separate sandbox for each layer.
Mail and file transfers aren't delayed, so work keeps moving.
No technical barriers
Analysis that catches even evasive threats, plugged straight in via MTA · ICAP · REST API.
Cost-efficient
No per-layer sandboxes. $0 in OS and Office licenses for analysis, starting from a 4-core server.
Business continuity
Mail and file transfers don't slow down. Add ZXONE Agent for ransomware blocking and recovery.
Frequently asked questions
No. ZX HUB integrates with what you have now, such as email security, NGFW, UTM and cross-domain solutions. It only adds unknown-threat analysis.
The average is 0.27 s per file (per KBeT testing). Even with hold-until-verdict as the default, users barely notice any wait.
We detected 99% of 250,000 MalwareBazaar samples from 2022 onward. The false-positive rate was 0% in validation on 260,000 clean files (over-detection cases found during validation were fed back into the engine).
No. A single ZX HUB analyzes four layers: email, network, cross-domain and endpoint (integration with each layer required).
From the KRW 10 million range, depending on the number of users (U100–U5000+). Delivered and installed as an all-in-one server, or as a cloud subscription.
Cloud PoCs can start right away. On-premises PoCs are arranged separately. We also run side-by-side demos with your own samples.
TTA GS Certification Grade 1 · KBeT V&V test certification · selected as a 2025 KISA excellent information security technology · 12 patents. CC certification is under review.